P1Security vulnerabilityPydantic AI
Early Found a Credential Leak. Pydantic Shipped the Fix.
The leak
Access tokens for connected services were written into tracing data in clear text, even with the privacy setting on. Anyone with dashboard access could read them.
The outcome
Early created a fix with a test and reported the issue privately. Pydantic confirmed it and shipped its own broader fix.
Step 1
Find the defect
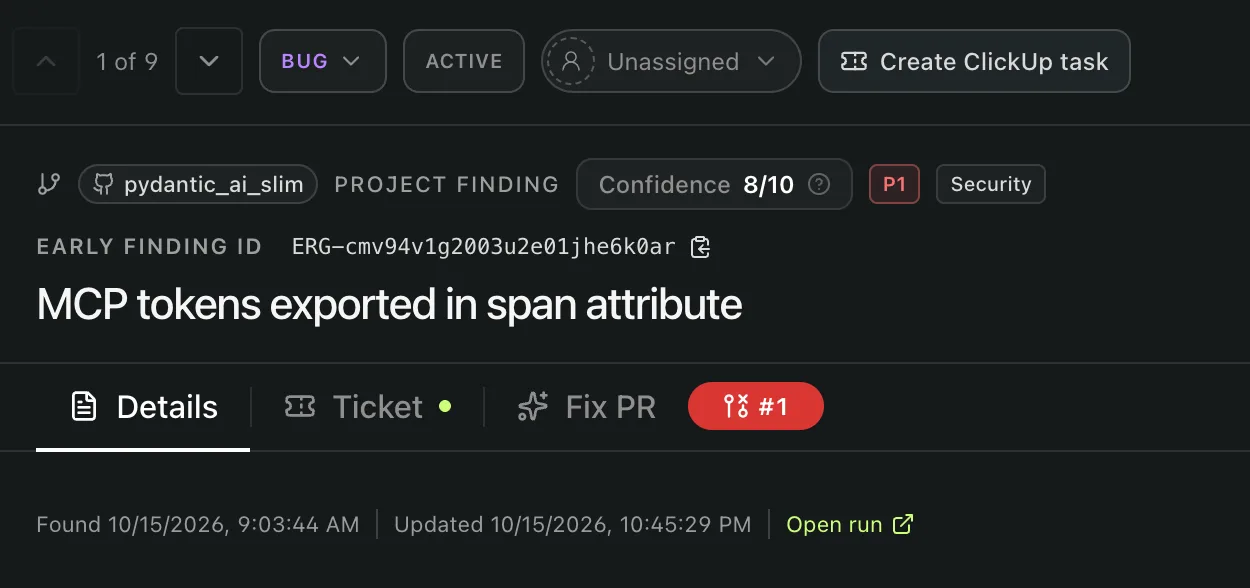
Early flagged a year-old credential leak while analyzing newer changes. It was the top finding of the run.
Step 2
Fix and test
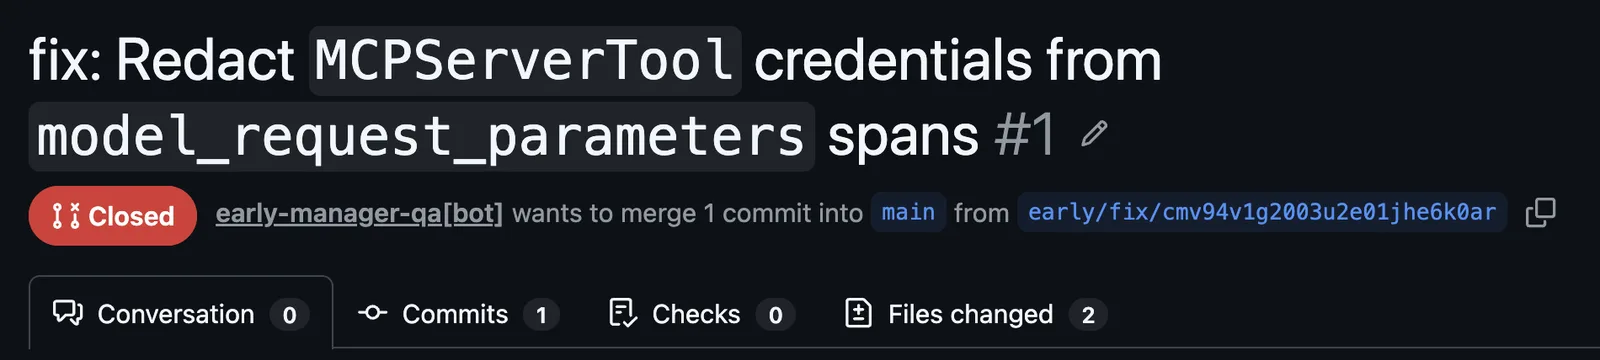
Early created a Fix PR with a test. It was closed on purpose so the issue could be disclosed privately first.
Step 3
Disclosed privately, fixed upstream
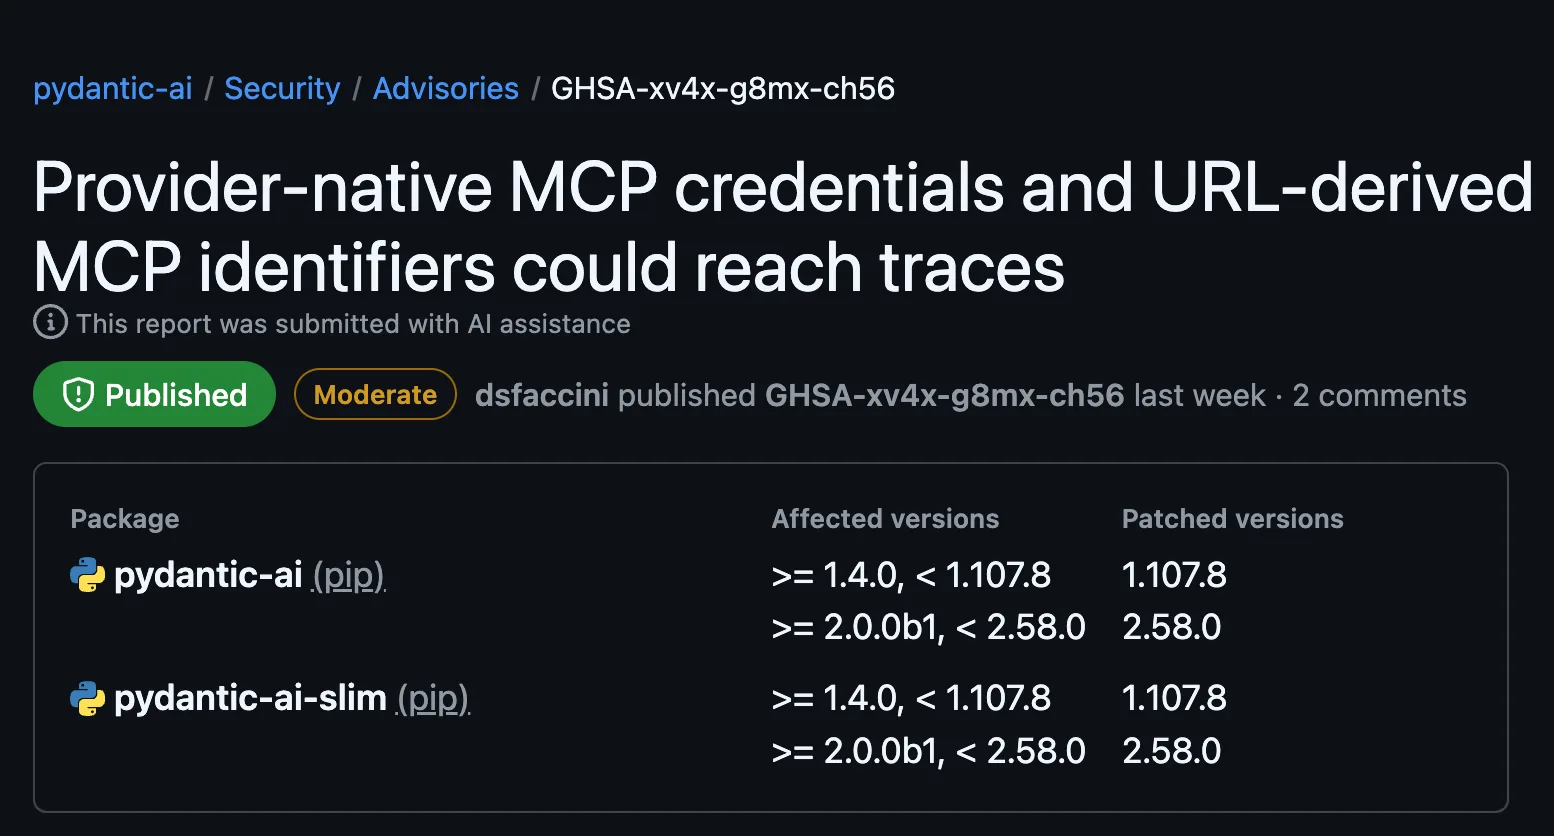
Pydantic confirmed the issue, published an advisory crediting the report, and released fixed versions.
Primary evidence
Follow the evidence.
 PHPRead case PHP2Shell backtrace defectHistorical replayFix PR generated
 MastraRead case Mastra output processor regression3 releases247 hours to fix
 RspackRead case Rspack CommonJS export regression1 release~18 hours to fix
 ConanRead case Conan no-op replacement regression1 release~20 hours to fix
 HonoRead case Hono form parsing regression3 releases12 days to fix